Zig
Zig
Oracle Cloud Secrets - Create or Update a Secret
See more Secrets Examples
Demonstrates how to create or update a secret stored in the Oracle Cloud Secrets.Note: This example requires Chilkat v10.1.0 or later.
Chilkat Zig Downloads
const std = @import("std");
const chilkat = @import("chilkat");
pub fn main(init: std.process.Init) !void {
const alloc = init.arena.allocator();
// This example requires the Chilkat API to have been previously unlocked.
// See Global Unlock Sample for sample code.
// The bootstrap secret will contain the following information:
// Private Key PEM
// See following examples for setting up a bootstrap secret in memory,
// or in the local manager (Windows Credentials Manager or Apple Keychain)
// Setup Bootstrap Secret in Local Manager
// Setup Bootstrap Secret in Memory
const bootstrap = try chilkat.Secrets.init();
defer bootstrap.deinit();
// Set the location of the bootstrap secret.
// Can be "local_manager" or "memory", depending on how you setup the bootstrap secret.
// ---------------------------------------------------------------------------------------------
// If your operating system is NOT Windows or MacOS/iOS, then change "local_manager" to "memory"
// You can also, if desired, use "memory" on Windows and MacOS/iOS if your bootstrap secret was previously setup in memory.
// ---------------------------------------------------------------------------------------------
bootstrap.setLocation("local_manager");
// Specify the bootstrap secret to be used.
const bs_id = try chilkat.JsonObject.init();
defer bs_id.deinit();
bs_id.updateString("appName", "oracle_bs") catch {};
bs_id.updateString("service", "Example") catch {};
bs_id.updateString("username", "Joe") catch {};
// ----------------------------------------------------
const secrets = try chilkat.Secrets.init();
defer secrets.deinit();
// Setup for the Oracle Cloud Secrets
secrets.setLocation("oracle_cloud");
secrets.setBootstrapSecret(bs_id, bootstrap) catch {
std.debug.print("{s}\n", .{try secrets.getLastErrorText(alloc)});
return;
};
// Let's create or update a secret in the Oracle Cloud Secrets.
// (The secret is updated if it already exists.)
const json = try chilkat.JsonObject.init();
defer json.deinit();
json.updateString("appName", "Test") catch {};
json.updateString("service", "Something") catch {};
json.updateString("domain", "Xyz") catch {};
json.updateString("username", "Abc") catch {};
// Oracle Cloud Secrets requires a lot of additional information for each API call.
// You'll need to replace the following with your values.
// Note: To learn how to find these values, go to an AI such as ChatGPT and ask (for example) "In Oracle Cloud, where do I find my master key OCID?"
json.updateString("vault_name", "ocid1.vault.oc1.us-chicago-1.ijttzlz7aadxo.abxxeljt4gv6tgrar66i5ugffincjmp52oveht3y2zn74rgo6raz6h72qtia") catch {};
json.updateString("region", "us-chicago-1") catch {};
json.updateString("tenancy_ocid", "ocid1.tenancy.oc1..aaaaaaaaov6vd3xdybgvwblezx2kmgjmo3dvsuljbwpf2m27mk47kkxsa5aa") catch {};
json.updateString("user_ocid", "ocid1.user.oc1..aaaaaaaarsn42gwcl5rvahcmt5r6aheek65z54k5nbd6gtclmqn6emkqxajq") catch {};
json.updateString("master_key_ocid", "ocid1.key.oc1.us-chicago-1.ijttzlz7aadxo.abxyeljtfbqhl5h2velmojmm6ls77lskmc7ardpekjgw264my6fuyxmhm6xa") catch {};
// Create or update the secret.
secrets.updateSecretStr(json, "This is the secret.") catch {
std.debug.print("{s}\n", .{try secrets.getLastErrorText(alloc)});
return;
};
std.debug.print("Success.\n", .{});
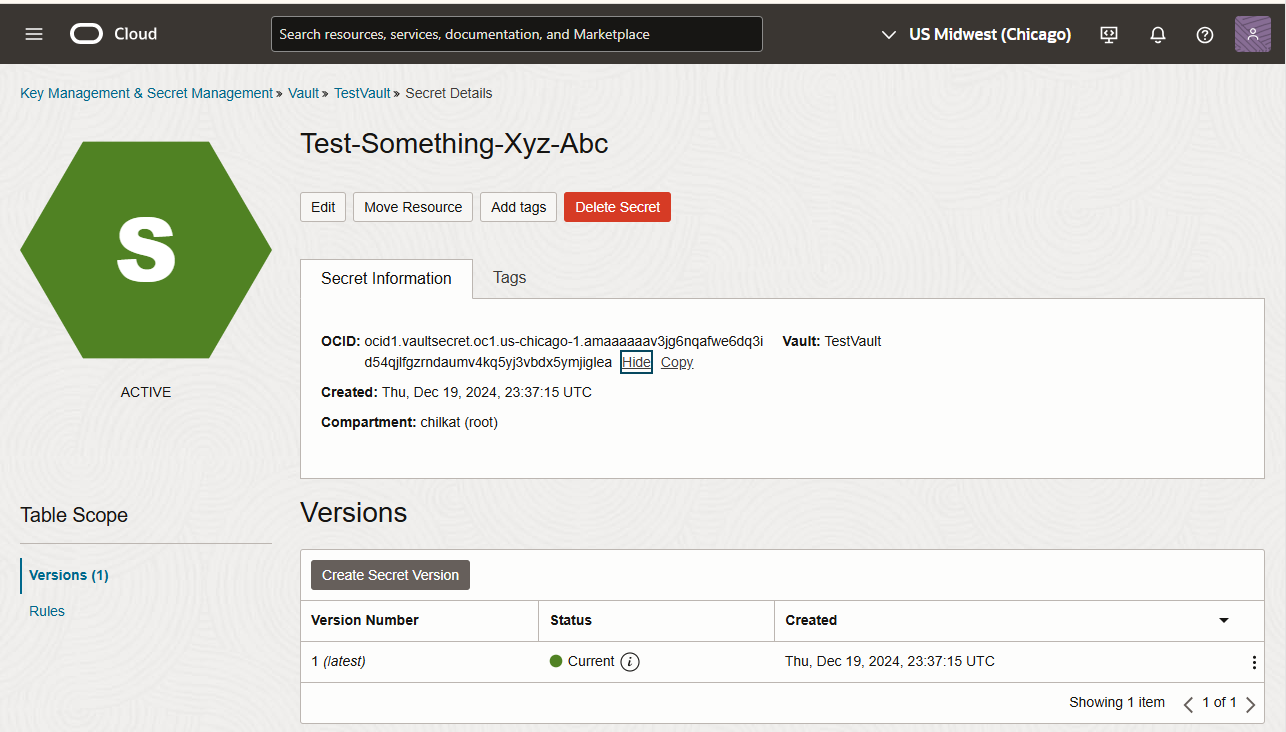
// Here you can see the secret that was created:
//  }