Zig Requires Chilkat v11.0.0+
Zig
ETrade OAuth1 Authorization (3-legged) Step 1
See more ETrade Examples
Demonstrates the first step in 3-legged OAuth1 authorization for the ETrade REST API. This example sends an HTTP request to the "request token URL" to get a request token that begins the OAuth1 process. (See https://apisb.etrade.com/docs/api/authorization/request_token.html )This example uses the sandbox request token URL. The live request token URL would be "https://api.etrade.com/oauth/request_token".
Chilkat Zig Downloads
const std = @import("std");
const chilkat = @import("chilkat");
pub fn main(init: std.process.Init) !void {
const alloc = init.arena.allocator();
var success: bool = false;
// This requires the Chilkat API to have been previously unlocked.
// See Global Unlock Sample for sample code.
const consumer_key = "ETRADE_CONSUMER_KEY";
const consumer_secret = "ETRADE_CONSUMER_SECRET";
// Note: This example uses the sandbox request token URL.
// The live Get Request Token Request URL is:
// https://api.etrade.com/oauth/request_token
// This example will use the Sandbox Token Request URL:
const request_token_url = "https://apisb.etrade.com/oauth/request_token";
const http = try chilkat.Http.init();
defer http.deinit();
success = true;
http.setOAuth1(true);
http.setOAuthConsumerKey(consumer_key);
http.setOAuthConsumerSecret(consumer_secret);
http.setOAuthCallback("oob");
const resp = try chilkat.HttpResponse.init();
defer resp.deinit();
http.httpNoBody("GET", request_token_url, resp) catch {
std.debug.print("{s}\n", .{try http.getLastErrorText(alloc)});
return;
};
// If successful, the resp.BodyStr contains something like this:
// oauth_token=-Wa_KwAAAAAAxfEPAAABV8Qar4Q&oauth_token_secret=OfHY4tZBX2HK4f7yIw76WYdvnl99MVGB&oauth_callback_confirmed=true
std.debug.print("{s}\n", .{try resp.getBodyStr(alloc)});
const hash_tab = try chilkat.Hashtable.init();
defer hash_tab.deinit();
hash_tab.addQueryParams(try resp.getBodyStr(alloc)) catch {};
const request_token = try hash_tab.lookupStr(alloc, "oauth_token");
const request_token_secret = try hash_tab.lookupStr(alloc, "oauth_token_secret");
http.setOAuthTokenSecret(request_token_secret);
std.debug.print("oauth_token = {s}\n", .{request_token});
std.debug.print("oauth_token_secret = {s}\n", .{request_token_secret});
// Save this request token for the next step..
const json = try chilkat.JsonObject.init();
defer json.deinit();
json.appendString("oauth_token", request_token) catch {};
json.appendString("oauth_token_secret", request_token_secret) catch {};
const fac = try chilkat.FileAccess.init();
defer fac.deinit();
fac.writeEntireTextFile("qa_data/tokens/etrade_request_token.json", try json.emit(alloc), "utf-8", false) catch {};
// ---------------------------------------------------------------------------
// The next step is to form a URL to send to the authorizeUrl
// This is an HTTP GET that we load into a popup browser.
const authorize_url = "https://us.etrade.com/e/t/etws/authorize";
const sb_url_for_browser = try chilkat.StringBuilder.init();
defer sb_url_for_browser.deinit();
sb_url_for_browser.append(authorize_url) catch {};
sb_url_for_browser.append("?key=") catch {};
sb_url_for_browser.append(consumer_key) catch {};
sb_url_for_browser.append("&token=") catch {};
sb_url_for_browser.append(request_token) catch {};
const url = try sb_url_for_browser.getAsString(alloc);
// Launch the system's default browser navigated to the URL.
const oauth2 = try chilkat.OAuth2.init();
defer oauth2.deinit();
oauth2.launchBrowser(url) catch {
std.debug.print("{s}\n", .{try oauth2.getLastErrorText(alloc)});
return;
};
// The ETrade account owner will login and grant access to the application.
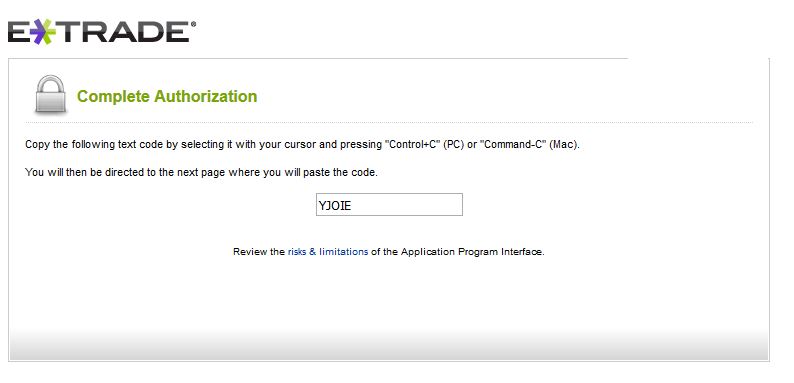
// A short verifier code will be displayed (as shown below), and this must be copy-and-pasted
// into the next step to Complete the 3-legged OAuth1 Authorization
// Note: The browser will NOT automatically direct you to the next page.
// You should copy the verifier code, close the browser, and then paste the verifier
// code into your application.
//  }