Zig
Zig
Using the ASN.1 API to Create a Certificate Request (CSR)
See more ASN.1 Examples
Note: This example requires Chilkat v9.5.0.50 or greater.This example demonstrates how to use the Chilkat ASN.1 API to create a certificate signing request. The purpose of this example is to show, in general, how to use the ASN.1 methods to create an ASN.1 document and save to DER. There may be more concise ways of creating a CSR rather than using the lower-level ASN.1 methods presented here. The hope is that this example will enable developers to create many different kinds of ASN.1 structures/documents for which no other means exist.
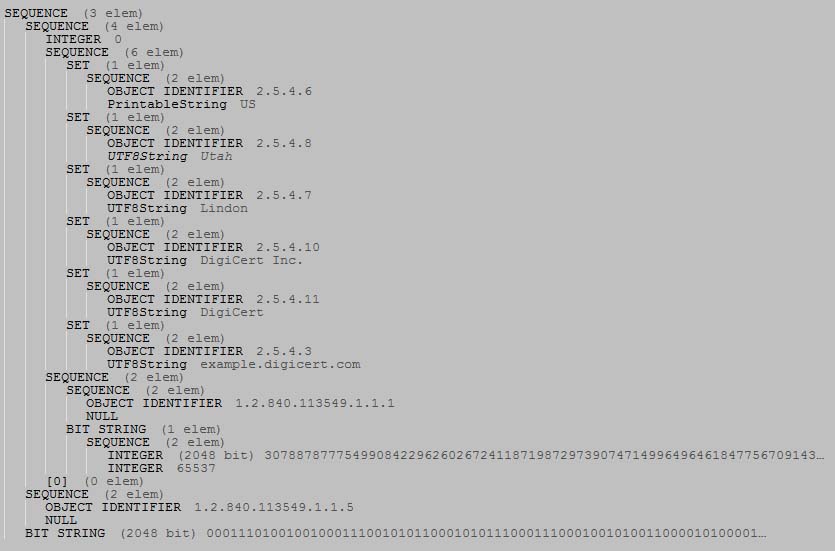
This example will create ASN.1 having this structure and content:
Chilkat Zig Downloads
const std = @import("std");
const chilkat = @import("chilkat");

pub fn main(init: std.process.Init) !void {
    const alloc = init.arena.allocator();

    // This example assumes the Chilkat API to have been previously unlocked.
    // See Global Unlock Sample for sample code.

    // A new ASN.1 object is automatically a SEQUENCE.
    // Given that the CSR's root item is a SEQUENCE, we can use
    // this as the root of our CSR.
    const asn_root = try chilkat.Asn.init();
    defer asn_root.deinit();

    // Beneath the root, we have a SEQUENCE (the certificate request info),
    // another SEQUENCE (the algorithm identifier), and a BITSTRING (this signature data)

    try asn_root.appendSequence();
    try asn_root.appendSequence();
    try asn_root.appendBits("1D2472B15C7129850E6C68C7435ED35508A92B03A8780BF979874D7270ADEE83849499C1BBC4B4E2B41B7F9DAF816CD755AE50DB79A9C2ECC796BCBA4E06E80287333BA12EC27B5D98E09905C6102A58438982DF24F7668086A485DBC3E88FDE598411781A40BD13C792C597FA2429B298C08A8D8B229638C8FB651FF0C5683F643191B39E71BA878B0C9FD94457FD6C8F8868251DD58ADF61C1C89771BCEC0BFEAF8F58570A910D3D150D5EEE2E0AA7DBD5C8D4FA5550D08F4069FDA7F797E90A3BBE90DA3F26D1B40D91ED72CA8D0685F685D678252ACB586F25A73D4053B6F7B39BD5A9691CFA19EE65A212E2708C13E28BA6BD33D1B7D27528DFD9418B5C", "hex");

    // ----------------------------------
    // Build the Certificate Request Info
    // ----------------------------------
    const asn_cert_req_info = try asn_root.getSubItem(0);
    defer asn_cert_req_info.deinit();
    try asn_cert_req_info.appendInt(0);

    // Build the Subject part of the Certificate Request Info
    const asn_cert_subject = try asn_cert_req_info.appendSequenceR();
    defer asn_cert_subject.deinit();

    // Add each subject part..
    var asn_temp: chilkat.Asn = try asn_cert_subject.appendSetR();
    defer asn_temp.deinit();
    try asn_temp.appendSequence2();
    // AppendSequence2 updates the internal reference to the newly appended SEQUENCE.
    // The OID and printable string are added to the SEQUENCE.
    try asn_temp.appendOid("2.5.4.6");
    try asn_temp.appendString("printable", "US");

    {
        const next = try asn_cert_subject.appendSetR();
        asn_temp.deinit();
        asn_temp = next;
    }
    try asn_temp.appendSequence2();
    try asn_temp.appendOid("2.5.4.8");
    try asn_temp.appendString("utf8", "Utah");

    {
        const next = try asn_cert_subject.appendSetR();
        asn_temp.deinit();
        asn_temp = next;
    }
    try asn_temp.appendSequence2();
    try asn_temp.appendOid("2.5.4.7");
    try asn_temp.appendString("utf8", "Lindon");

    {
        const next = try asn_cert_subject.appendSetR();
        asn_temp.deinit();
        asn_temp = next;
    }
    try asn_temp.appendSequence2();
    try asn_temp.appendOid("2.5.4.10");
    try asn_temp.appendString("utf8", "DigiCert Inc.");

    {
        const next = try asn_cert_subject.appendSetR();
        asn_temp.deinit();
        asn_temp = next;
    }
    try asn_temp.appendSequence2();
    try asn_temp.appendOid("2.5.4.11");
    try asn_temp.appendString("utf8", "DigiCert");

    {
        const next = try asn_cert_subject.appendSetR();
        asn_temp.deinit();
        asn_temp = next;
    }
    try asn_temp.appendSequence2();
    try asn_temp.appendOid("2.5.4.3");
    try asn_temp.appendString("utf8", "example.digicert.com");

    // Build the Public Key Info part of the Certificate Request Info
    const asn_pub_key_info = try asn_cert_req_info.appendSequenceR();
    defer asn_pub_key_info.deinit();

    const asn_pub_key_alg_id = try asn_pub_key_info.appendSequenceR();
    defer asn_pub_key_alg_id.deinit();
    try asn_pub_key_alg_id.appendOid("1.2.840.113549.1.1.1");
    try asn_pub_key_alg_id.appendNull();

    // The public key itself is a BIT STRING, but the bit string is composed of ASN.1
    // for the RSA public key.  We'll first build the RSA ASN.1 for the public key
    // (containing the 2048 bit modulus and exponent), and encoded it to DER, and then add
    // the DER bytes as a BIT STRING (as a sub-item of asnPubKeyInfo)

    // This is already a SEQUENCE..
    const asn_rsa_key = try chilkat.Asn.init();
    defer asn_rsa_key.deinit();

    // The RSA modulus is a big integer.
    try asn_rsa_key.appendBigInt("F3E4E8EDDFB690F59E06FFE8AD4DCB55B2700EB4906DE29A9829A8C29E5BA83C48C15DB4CEA45BEC03D438A62854414538442CE93EA02269C8A2585B887EA6E33819FC23EF5813A465CF9CD4FA36126BC1CFE003E6C05D4F993319003A35B5B264695DC51B6134B3ACD5E7CE85D9D616E848D7ADAA99C7E5829888583BB0AB80BD7FE62478984D9FD745E7EA309BC70E4260EB57C34D7624EA8A7F2ADEA6001C72515B6F209495026644D9C0869247A72B050F136D8344D1D73E09A6B70CE224CF510EB075B34F1FA7D3329FA9C6E05E2E03271F82D5B8E9B583D104F64BF0301E5AE03C79BB9D553E38C84A7CD86F7AFC681C7FB177DF13317B4C9CF976BAA3", "hex");
    try asn_rsa_key.appendInt(65537);

    const rsa_key_der_base64 = try asn_rsa_key.getEncodedDer(alloc, "base64");

    // Now add the RSA key DER as a BIT STRING.
    try asn_pub_key_info.appendBits(rsa_key_der_base64, "base64");

    // The last part of the certificate request info is an empty context-specific constructed item
    // with a tag equal to 0.
    try asn_cert_req_info.appendContextConstructed(0);

    // ----------------------------------
    // Finally, add the algorithm identifier, which is the 2nd sub-item under the root.
    // ----------------------------------
    const asn_alg_id = try asn_root.getSubItem(1);
    defer asn_alg_id.deinit();
    try asn_alg_id.appendOid("1.2.840.113549.1.1.5");
    try asn_alg_id.appendNull();

    // Write the CSR to a DER encoded binary file:
    asn_root.writeBinaryDer("qa_output/csr.der") catch {
        std.debug.print("{s}\n", .{try asn_root.getLastErrorText(alloc)});
        return;
    };

    // It is also possible to get the CSR in base64 format:
    const csr_base64 = try asn_root.getEncodedDer(alloc, "base64");

    std.debug.print("Base64 CSR:\n", .{});
    std.debug.print("{s}\n", .{csr_base64});

    // To emit as PEM:
    // (Note: The pem.AddItem method was added in Chilkat v9.5.0.59)
    const pem = try chilkat.Pem.init();
    defer pem.deinit();
    pem.addItem("csr", "base64", csr_base64) catch {};
    std.debug.print("PEM:\n", .{});
    std.debug.print("{s}\n", .{try pem.toPem(alloc)});
}