Xbase++ Requires Chilkat v10.1.2+
Xbase++
Rabobank OAuth2 Access Token
See more OAuth2 Examples
Demonstrates how to get an OAuth 2.0 access token to access Rabobank API'sImportant: This example is for desktop apps only. (It is not for web-based applications.)
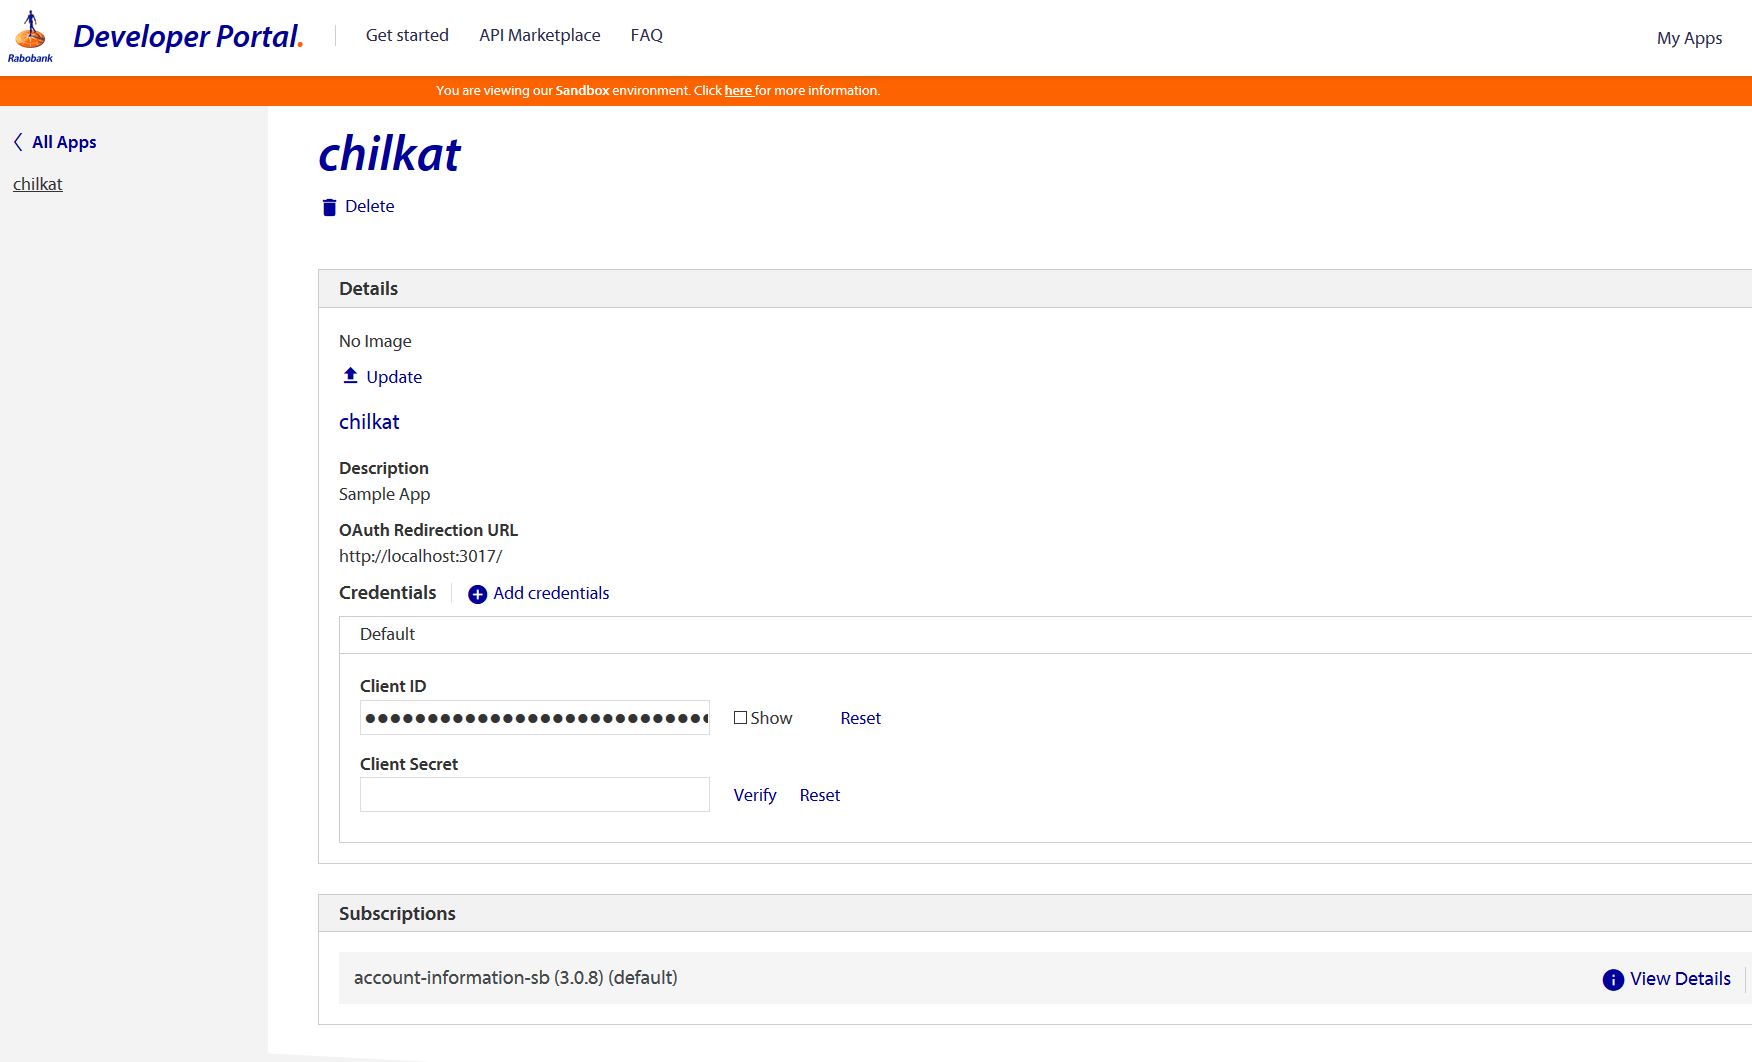
Your app defined in the Rabobank portal should look something like this. (Our test app is named "chilkat". You should name your app something else.)
Chilkat Xbase++ Downloads
LOCAL nSuccess
LOCAL oOauth2
LOCAL cUrl
LOCAL nNumMsWaited
LOCAL oJson
LOCAL oFac

nSuccess := 0

//  For more information about the OAuth2, see OAuth 2.0 Authorization Flow

oOauth2 := CreateObject("Chilkat.OAuth2")

//  This should be the port in the localhost callback URL for your app.
//  The callback URL would look like "http://localhost:3017/" if the port number is 3017.
oOauth2:ListenPort := 3017

//  IMPORTANT: Don't forget to subscribe your Rabobank application to the OAuth 2.0 services in the Rabobank Online Developer Portal.
//  IMPORTANT: Don't forget to subscribe your Rabobank application to the OAuth 2.0 services in the Rabobank Online Developer Portal.
//  IMPORTANT: Don't forget to subscribe your Rabobank application to the OAuth 2.0 services in the Rabobank Online Developer Portal.
//  IMPORTANT: Don't forget to subscribe your Rabobank application to the OAuth 2.0 services in the Rabobank Online Developer Portal.

//  See also https://developer.rabobank.nl/faq

oOauth2:AuthorizationEndpoint := "https://api-sandbox.rabobank.nl/openapi/sandbox/oauth2/authorize"
oOauth2:TokenEndpoint := "https://api-sandbox.rabobank.nl/openapi/sandbox/oauth2/token"

//  Replace these with actual values.
oOauth2:ClientId := "YOUR_APP_CLIENT_ID"
//  This is your app password:
oOauth2:ClientSecret := "YOUR_APP_CLIENT_SECRET"

oOauth2:CodeChallenge := 0
//  Provide a SPACE separated list of scopes, as defined in the Rabobank API documentation,
//  such as at https://developer-sandbox.rabobank.nl/reference/accounts-ais-sb/3-0-8

//  Important: To get a refresh token in the final response, you have to ask for "offline_access" scope
oOauth2:Scope := "ais.balances.read ais.transactions.read-90days ais.transactions.read-history"

//  Begin the OAuth2 Authorization code flow.  This returns a URL that should be loaded in a browser.
cUrl := oOauth2:StartAuth()
IF (oOauth2:LastMethodSuccess != 1)
    ? oOauth2:LastErrorText
    oOauth2:destroy()
    RETURN
ENDIF

? "url = " + cUrl

//  Launch the default browser on the system and navigate to the url.
//  The LaunchBrowser method was added in Chilkat v10.1.2.
nSuccess := oOauth2:LaunchBrowser(cUrl)
IF (nSuccess == 0)
    ? oOauth2:LastErrorText
    oOauth2:destroy()
    RETURN
ENDIF

//  Wait for the user to approve or deny authorization in the browser.
nNumMsWaited := 0
DO WHILE (nNumMsWaited < 90000) .AND. (oOauth2:AuthFlowState < 3)
    oOauth2:SleepMs(100)
    nNumMsWaited := nNumMsWaited + 100
ENDDO

//  If the browser does not respond within the specified time, AuthFlowState will be:
//
//  1: Waiting for Redirect - The OAuth2 background thread is waiting for the browser's redirect request.
//  2: Waiting for Final Response - The thread is awaiting the final access token response.
//  In either case, cancel the background task initiated by StartAuth.

IF (oOauth2:AuthFlowState < 3)
    oOauth2:Cancel()
    ? "No response from the browser!"
    oOauth2:destroy()
    RETURN
ENDIF

//  Check AuthFlowState to determine if authorization was granted, denied, or failed:
//
//  3: Success - OAuth2 flow completed, the background thread exited, and the successful response is in AccessTokenResponse.
//  4: Access Denied - OAuth2 flow completed, the background thread exited, and the error response is in AccessTokenResponse.
//  5: Failure - OAuth2 flow failed before completion, the background thread exited, and error details are in FailureInfo.

IF (oOauth2:AuthFlowState == 5)
    ? "OAuth2 failed to complete."
    ? oOauth2:FailureInfo
    oOauth2:destroy()
    RETURN
ENDIF

IF (oOauth2:AuthFlowState == 4)
    ? "OAuth2 authorization was denied."
    ? oOauth2:AccessTokenResponse
    oOauth2:destroy()
    RETURN
ENDIF

IF (oOauth2:AuthFlowState != 3)
    ? "Unexpected AuthFlowState:" + Str(oOauth2:AuthFlowState)
    oOauth2:destroy()
    RETURN
ENDIF

? "OAuth2 authorization granted!"
? "Access Token = " + oOauth2:AccessToken

//  Get the full JSON response:
oJson := CreateObject("Chilkat.JsonObject")
oJson:Load(oOauth2:AccessTokenResponse)
oJson:EmitCompact := 0

//  The JSON response looks like this:

//  {
//    "token_type": "Bearer",
//    "access_token": "AAIkYTU0ZWM ... sxE0KL0HHWw",
//    "expires_in": 3600,
//    "consented_on": 1584641121,
//    "scope": "ais.balances.read ais.transactions.read-90days ais.transactions.read-history",
//    "refresh_token": "AAJXXSdN ... Uiblz9ILkxNBlytRGA",
//    "refresh_token_expires_in": 157784760,
//    "expires_on": "1584644722"
//  }

? oJson:Emit()

//  Save the JSON to a file to be used in future requests.
oFac := CreateObject("Chilkat.FileAccess")
oFac:WriteEntireTextFile("qa_data/tokens/rabobank.json", oJson:Emit(), "utf-8", 0)

oOauth2:destroy()
oJson:destroy()
oFac:destroy()