Tcl Requires Chilkat v9.5.0.85+
Tcl
Sign PDF with Timestamp from TSA (Timestamp Server Authority)
See more PDF Signatures Examples
This example demonstrates how to a sign a PDF that is both long-term validation (LTV) enabled and includes a validating timestamp from a TSA (Timestamp Server Authority).Chilkat Tcl Downloads
load ./chilkat.dll
set success 0
# This example requires the Chilkat API to have been previously unlocked.
# See Global Unlock Sample for sample code.
set pdf [new_CkPdf]
# Load a PDF to be signed.
# The "hello.pdf" is available at https://chilkatsoft.com/hello.pdf
set success [CkPdf_LoadFile $pdf "qa_data/pdf/hello.pdf"]
if {$success == 0} then {
puts [CkPdf_lastErrorText $pdf]
delete_CkPdf $pdf
exit
}
# Options for signing are specified in JSON.
set json [new_CkJsonObject]
# In most cases, the signingCertificateV2 and signingTime attributes are required.
CkJsonObject_UpdateInt $json "signingCertificateV2" 1
CkJsonObject_UpdateInt $json "signingTime" 1
# Tell Chilkat to create an LTV-enabled (long term validation) signature.
# See PDF Long-Term Validation (LTV) Signature Example for more detailed comments about "ltvOcsp".
CkJsonObject_UpdateBool $json "ltvOcsp" 1
# Tell Chilkat to request a timestamp from a TSA server and include the timestamp token (1.2.840.113549.1.9.16.2.14)
# in the CMS signature's authentication attributes
CkJsonObject_UpdateBool $json "timestampToken.enabled" 1
# In this example, we'll use a free TSA server (timestamp.digicert.com), but you may want to use your own timestamp authority server.
CkJsonObject_UpdateString $json "timestampToken.tsaUrl" "http://timestamp.digicert.com"
# If the timestamp server requires a username/password, do the following. Otherwise omit the following few lines of code.
CkJsonObject_UpdateString $json "timestampToken.tsaUsername" "the_tsa_username"
CkJsonObject_UpdateString $json "timestampToken.tsaPassword" "the_tsa_password"
# When requesting the timestamp token, ask the server to include its certificate in the timestamp token response.
# This allows for the timestamp server's certificate to be included in the LTV validation (i.e. if the timestamp server
# has an OCSP URL, then Chilkat will also do the OCSP request for the timestamp server's certificate.)
CkJsonObject_UpdateBool $json "timestampToken.requestTsaCert" 1
# Define the appearance of the signature.
CkJsonObject_UpdateInt $json "page" 1
CkJsonObject_UpdateString $json "appearance.y" "top"
CkJsonObject_UpdateString $json "appearance.x" "left"
CkJsonObject_UpdateString $json "appearance.fontScale" "10.0"
CkJsonObject_UpdateString $json "appearance.text[0]" "Digitally signed by: cert_cn"
CkJsonObject_UpdateString $json "appearance.text[1]" "current_dt"
CkJsonObject_UpdateString $json "appearance.text[2]" "This is an LTV-enabled signature with a TSA timestamp."
# Load the signing certificate. (Use your own certificate.)
set cert [new_CkCert]
set success [CkCert_LoadPfxFile $cert "qa_data/pfx/myPdfSigningCert.pfx" "pfxPassword"]
if {$success == 0} then {
puts [CkCert_lastErrorText $cert]
delete_CkPdf $pdf
delete_CkJsonObject $json
delete_CkCert $cert
exit
}
# Tell the pdf object to use the certificate for signing.
set success [CkPdf_SetSigningCert $pdf $cert]
if {$success == 0} then {
puts [CkPdf_lastErrorText $pdf]
delete_CkPdf $pdf
delete_CkJsonObject $json
delete_CkCert $cert
exit
}
set success [CkPdf_SignPdf $pdf $json "qa_output/hello_ltv_signed_with_timestamp.pdf"]
if {$success == 0} then {
puts [CkPdf_lastErrorText $pdf]
delete_CkPdf $pdf
delete_CkJsonObject $json
delete_CkCert $cert
exit
}
puts "The PDF has been successfully cryptographically signed with TSA timestamp and long-term validation."
# If you open the Signature Panel in Adobe Acrobat, it will indicate that the signature is LTV enabled
# and contains an embedded timestamp:
# 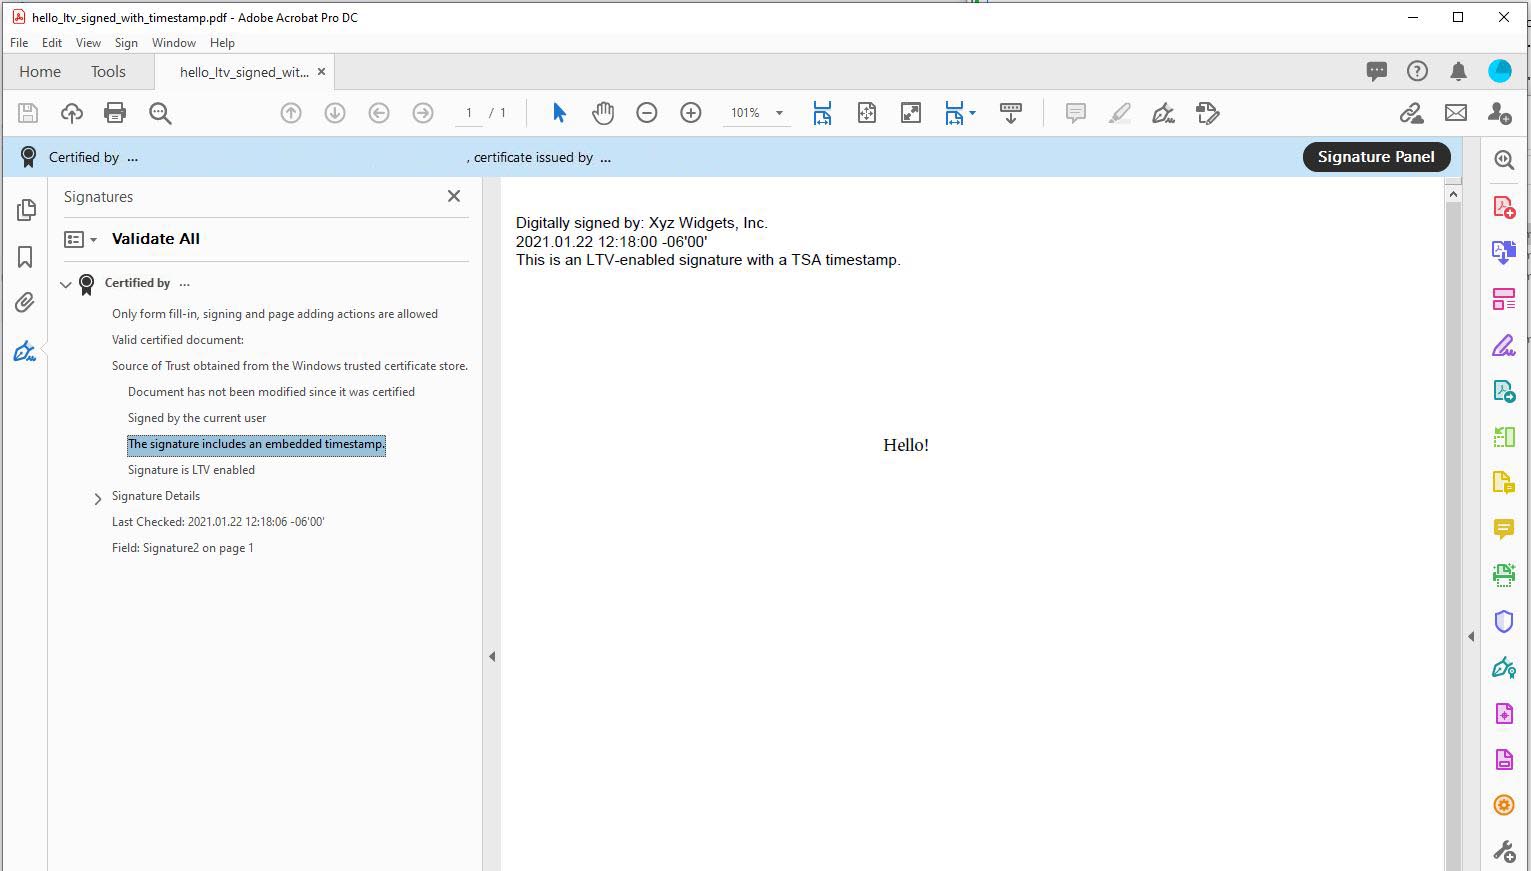 delete_CkPdf $pdf
delete_CkJsonObject $json
delete_CkCert $cert