Swift
Swift
Sign PDF: Choosing RSASSA-PSS or PKCS1-v1_5 and Hash Algorithm
See more PDF Signatures Examples
This example demonstrates how to choose between RSASSA-PSS vs. PKCS1-v1_5 and the hash algorithm when signing a PDF.Chilkat Swift Downloads
func chilkatTest() {
var success: Bool = false
// This example requires the Chilkat API to have been previously unlocked.
// See Global Unlock Sample for sample code.
let pdf = CkoPdf()!
// Load a PDF to be signed.
// The "hello.pdf" is available at https://chilkatsoft.com/hello.pdf
success = pdf.loadFile(filePath: "qa_data/pdf/hello.pdf")
if success == false {
print("\(pdf.lastErrorText!)")
return
}
// Options for signing are specified in JSON.
let json = CkoJsonObject()!
// In most cases, the signingCertificateV2 attribute is needed.
json.updateInt(jsonPath: "signingCertificateV2", value: 1)
// ---------------------------------------------------------------------------------------------------------------------------
// This example is the same as the example at Sign a PDF (Simplest Example Possible)
// but with the following lines added to specify the signature scheme and hash algorithm.
// The signature schemes PKCS-v1_5 and RSASSA-PSS have differences.
// PKCSV1_5 is deterministic. The same message and key will produce an identical signature value each time.
// PSS is randomized and will produce a different signature value each time.
// To choose the hash algorithm:
// (The typical choices are sha1, sha256, sha384, and sha512.)
json.updateString(jsonPath: "hashAlgorithm", value: "sha256")
// To choose PKCSV1_5:
json.updateString(jsonPath: "signingAlgorithm", value: "pkcs")
// Alternatively, to choose RSASSA-PSS:
json.updateString(jsonPath: "signingAlgorithm", value: "pss")
// If not specified, the default is SHA256 with PKCS-v1_5.
// The remainder of this example is the same as the example at Sign a PDF (Simplest Example Possible)
// ---------------------------------------------------------------------------------------------------------------------------
// Put the signature on page 1, top left
json.updateInt(jsonPath: "page", value: 1)
json.updateString(jsonPath: "appearance.y", value: "top")
json.updateString(jsonPath: "appearance.x", value: "left")
// Use a font scale of 10.0
json.updateString(jsonPath: "appearance.fontScale", value: "10.0")
// In this example, the appearance of the digital signature will contain three lines:
// 1) The signing certificate's common name
// 2) The current date/time
// 3) Some arbitrary text.
// The keyword "cert_cn" is replaced with the Certificate's Subject Common Name.
// The keyword "current_dt" is replaced with the current date/time.
// Any number of appearance text lines can be added.
json.updateString(jsonPath: "appearance.text[0]", value: "Digitally signed by: cert_cn")
json.updateString(jsonPath: "appearance.text[1]", value: "current_dt")
json.updateString(jsonPath: "appearance.text[2]", value: "The crazy brown fox jumps over the lazy dog.")
// Load the signing certificate. (Use your own certificate.)
let cert = CkoCert()!
success = cert.loadPfxFile(path: "qa_data/pfx/myPdfSigningCert.pfx", password: "secret")
if success == false {
print("\(cert.lastErrorText!)")
return
}
// Tell the pdf object to use the certificate for signing.
success = pdf.setSigningCert(cert: cert)
if success == false {
print("\(pdf.lastErrorText!)")
return
}
success = pdf.sign(jsonOptions: json, outFilePath: "qa_output/hello_signed.pdf")
if success == false {
print("\(pdf.lastErrorText!)")
return
}
print("The PDF has been successfully cryptographically signed.")
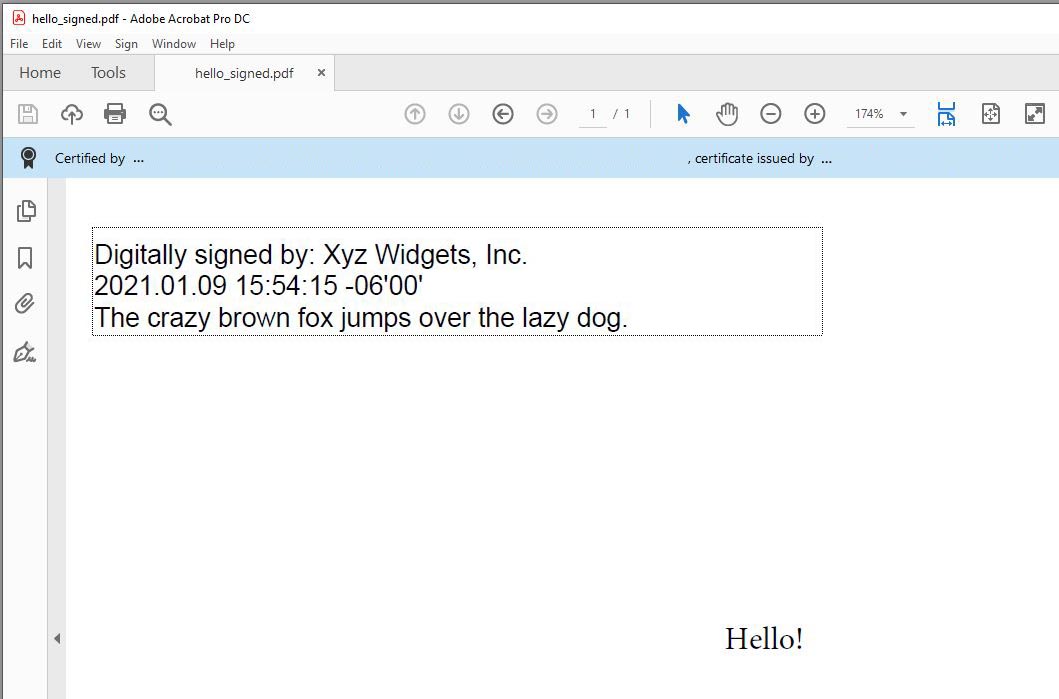
// The appearance of the signature appears in Adobe Acrobat as shown here:
//  }