React Native Requires Chilkat v10.1.2+
React Native
X.com OAuth 2.0 Authorization Code with PKCE
See more X Examples
Demonstrates how to get an X.com OAuth2 access token from a desktop application or script.Chilkat React Native Downloads
import { CkDateTime, JsonObject, OAuth2 } from '@chilkat/react-native'
function chilkatExample() {
// For more information about the OAuth2, see OAuth 2.0 Authorization Flow
const oauth2 = new OAuth2();
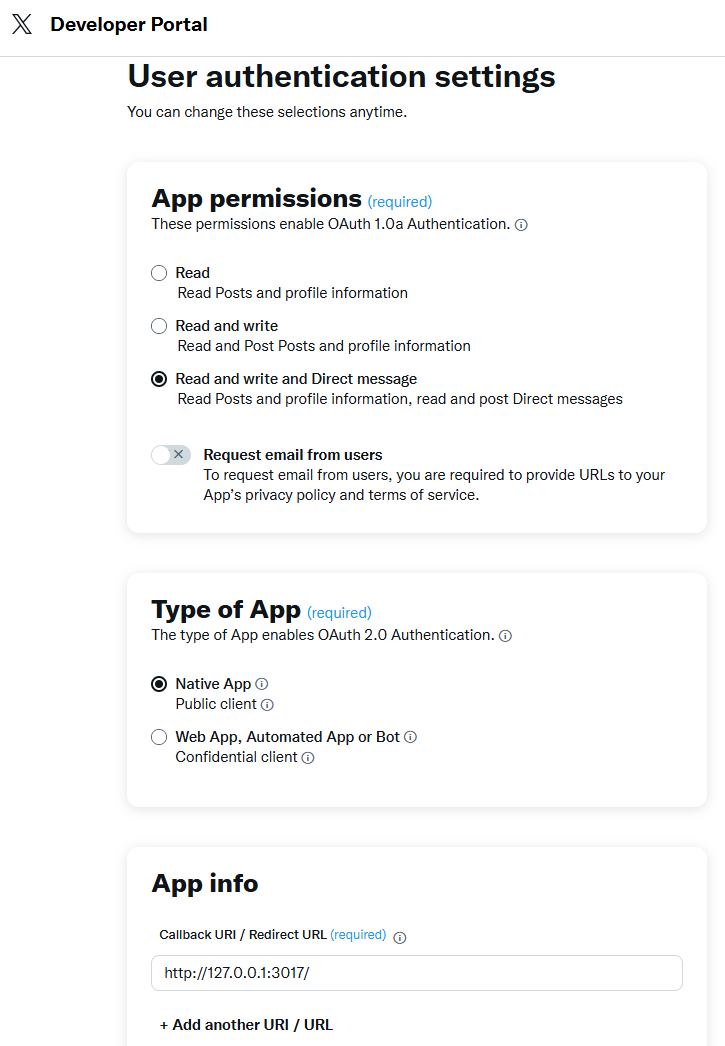
// The port should match the Authorized Redirect URL in your X.com app,
// which would look like "http://127.0.0.1:3017/"
// See the screenshot below of the App Settings in the X Developer Portal
oauth2.localHost = '127.0.0.1';
oauth2.listenPort = 3017;
oauth2.authorizationEndpoint = 'https://x.com/i/oauth2/authorize';
oauth2.tokenEndpoint = 'https://api.x.com/2/oauth2/token';
// Replace this with your actual X.com OAuth2 Client ID and Client Secret
oauth2.clientId = 'OAUTH2_CLIENT_ID';
oauth2.clientSecret = 'OAUTH2_CLIENT_SECRET';
// This is for Require Proof Key for Code Exchange (PKCE)
// See OAuth2 PKCE Explained
oauth2.codeChallenge = true;
oauth2.codeChallengeMethod = 'S256';
// Space separated scopes...
oauth2.scope = 'tweet.read tweet.write users.read follows.read follows.write offline.access like.read like.write block.read block.write';
// Begin the OAuth2 Authorization code flow. This returns a URL that should be loaded in a browser.
let url: string;
try {
url = oauth2.startAuth();
} catch {
console.log(oauth2.lastErrorText);
return;
}
console.log(`url = ${url}`);
// Launch the default browser on the system and navigate to the url.
// The LaunchBrowser method was added in Chilkat v10.1.2.
try {
oauth2.launchBrowser(url);
} catch {
console.log(oauth2.lastErrorText);
return;
}
// Wait for the user to approve or deny authorization in the browser.
let numMsWaited = 0;
while ((numMsWaited < 10000) && (oauth2.authFlowState < 3)) {
oauth2.sleepMs(100);
numMsWaited += 100;
}
// If the browser does not respond within the specified time, AuthFlowState will be:
//
// 1: Waiting for Redirect - The OAuth2 background thread is waiting for the browser's redirect request.
// 2: Waiting for Final Response - The thread is awaiting the final access token response.
// In either case, cancel the background task initiated by StartAuth.
if (oauth2.authFlowState < 3) {
oauth2.cancel();
console.log('No response from the browser!');
return;
}
// Check AuthFlowState to determine if authorization was granted, denied, or failed:
//
// 3: Success - OAuth2 flow completed, the background thread exited, and the successful response is in AccessTokenResponse.
// 4: Access Denied - OAuth2 flow completed, the background thread exited, and the error response is in AccessTokenResponse.
// 5: Failure - OAuth2 flow failed before completion, the background thread exited, and error details are in FailureInfo.
if (oauth2.authFlowState === 5) {
console.log('OAuth2 failed to complete.');
console.log(oauth2.failureInfo);
return;
}
if (oauth2.authFlowState === 4) {
console.log('OAuth2 authorization was denied.');
console.log(oauth2.accessTokenResponse);
return;
}
if (oauth2.authFlowState !== 3) {
console.log(`Unexpected AuthFlowState:${oauth2.authFlowState}`);
return;
}
console.log('OAuth2 authorization granted!');
const json = new JsonObject();
json.load(oauth2.accessTokenResponse);
json.emitCompact = false;
// If an "expires_on" member does not exist, then add the JSON member by
// getting the current system date/time and adding the "expires_in" seconds.
// This way we'll know when the token expires.
if (!json.hasMember('expires_on')) {
const dtExpire = new CkDateTime();
dtExpire.setFromCurrentSystemTime();
dtExpire.addSeconds(json.intOf('expires_in'));
json.appendString('expires_on', dtExpire.getAsUnixTimeStr(false));
}
console.log(`Access Token Response = ${json.emit()}`);
// A sample access token response:
// {
// "token_type": "bearer",
// "expires_in": 7200,
// "access_token": "VmNDLVZiYUZwejY5Mkx3RblFTmo3ek1leTRGclMuZFVOUTVUTWpNbVZKb1N5OjE3NDAxNjk4MDVxNTE6MToxOaF0OjE",
// "scope": "block.read follows.read offline.access tweet.write block.write like.write like.read users.read tweet.read follows.write",
// "refresh_token": "eThOWVVFSTRqdVp3QTFndGsxM2ZGZmFyNWVrU0phM1JKbGdrbGNWRGJzb1loOjE3NDAwMjk4MDUxNTI6MTowOnJ0OjE"
// }
console.log(`Access Token = ${oauth2.accessToken}`);
console.log(`Refresh Token = ${oauth2.refreshToken}`);
// Save the JSON access token response to a file for subsequent use..
json.writeFile('qa_data/tokens/x.json');
//  }