Delphi DLL Requires Chilkat v10.1.0+
Delphi DLL
Azure Key Vault - Create or Update a JSON Secret
See more Secrets Examples
Demonstrates how to create or update a JSON secret stored in the Azure Key Vault.Chilkat Delphi DLL Downloads
var
success: Boolean;
bootstrap: HCkSecrets;
bsId: HCkJsonObject;
secrets: HCkSecrets;
json: HCkJsonObject;
jsonSecret: HCkJsonObject;
begin
success := False;
// This example requires the Chilkat API to have been previously unlocked.
// See Global Unlock Sample for sample code.
// The bootstrap secret will contain the following information:
// Azure Tenant ID
// Azure Client ID
// Azure Client Secret
// See following examples for setting up a bootstrap secret in memory,
// or in the local manager (Windows Credentials Manager or Apple Keychain)
// Setup Bootstrap Secret in Local Manager
// Setup Bootstrap Secret in Memory
bootstrap := CkSecrets_Create();
// Set the location of the bootstrap secret.
// Can be "local_manager" or "memory", depending on how you setup the bootstrap secret.
// ---------------------------------------------------------------------------------------------
// If your operating system is NOT Windows or MacOS/iOS, then change "local_manager" to "memory"
// You can also, if desired, use "memory" on Windows and MacOS/iOS if your bootstrap secret was previously setup in memory.
// ---------------------------------------------------------------------------------------------
CkSecrets_putLocation(bootstrap,'local_manager');
// Specify the bootstrap secret to be used.
bsId := CkJsonObject_Create();
CkJsonObject_UpdateString(bsId,'appName','azure_bs');
CkJsonObject_UpdateString(bsId,'service','Example');
CkJsonObject_UpdateString(bsId,'username','Joe');
// ----------------------------------------------------
secrets := CkSecrets_Create();
CkSecrets_putLocation(secrets,'azure_key_vault');
success := CkSecrets_SetBootstrapSecret(secrets,bsId,bootstrap);
if (success = False) then
begin
Memo1.Lines.Add(CkSecrets__lastErrorText(secrets));
Exit;
end;
// ----
// Specify the name of the secret.
// service and username are required.
// appName and domain are optional.
// Note: The values are arbitrary and can be anything you want.
json := CkJsonObject_Create();
CkJsonObject_UpdateString(json,'appName','MyApp');
CkJsonObject_UpdateString(json,'service','OAuth2');
CkJsonObject_UpdateString(json,'domain','onedrive');
CkJsonObject_UpdateString(json,'username','matt');
// For Azure Key Vault, we also need to specify the name of the vault where the secret is to be stored.
// Replace "kvChilkat" with the name of your key vault.
CkJsonObject_UpdateString(json,'vaultName','kvChilkat');
// Get the secret to be stored.
jsonSecret := CkJsonObject_Create();
success := CkJsonObject_LoadFile(jsonSecret,'qa_data/tokens/oneDrive.json');
if (success = False) then
begin
Memo1.Lines.Add(CkJsonObject__lastErrorText(jsonSecret));
Exit;
end;
// Create or update the secret.
success := CkSecrets_UpdateSecretJson(secrets,json,jsonSecret);
if (success = False) then
begin
Memo1.Lines.Add(CkSecrets__lastErrorText(secrets));
Exit;
end;
Memo1.Lines.Add('Success.');
// Here you can see the secret that was created:
// 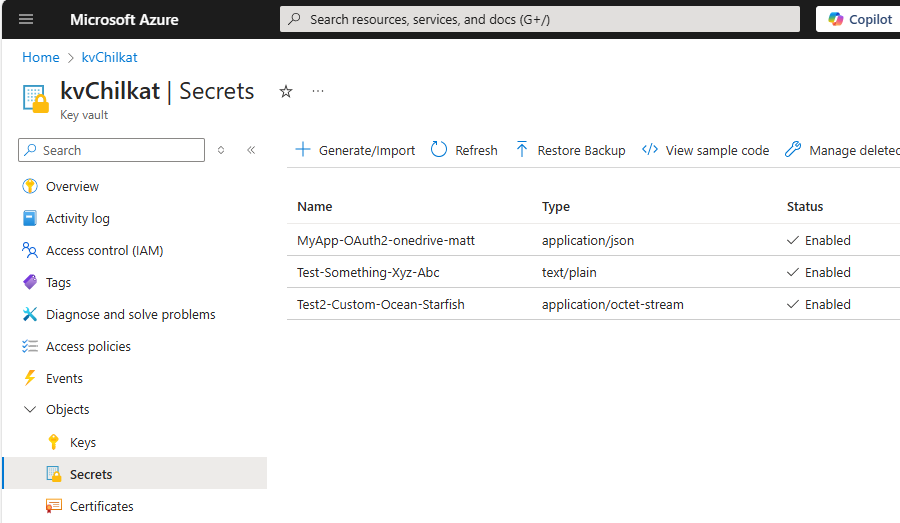 CkSecrets_Dispose(bootstrap);
CkJsonObject_Dispose(bsId);
CkSecrets_Dispose(secrets);
CkJsonObject_Dispose(json);
CkJsonObject_Dispose(jsonSecret);