DataFlex
DataFlex
ScMinidriver - Get Public Keys from Smart Card Key Container
See more ScMinidriver Examples
Demonstrates how to query a key container on a smart card (or USB token) to get the public part of the private keys that are present. A key container can hold two separate private keys -- one in the "signature" position, and the other in the "key exchange" position.Chilkat DataFlex Downloads
Use ChilkatAx-win32.pkg
Procedure Test
Boolean iSuccess
Handle hoScmd
String sReaderName
Variant vPubkey_sig
Handle hoPubkey_sig
Variant vPubkey_kex
Handle hoPubkey_kex
String sTemp1
Boolean bTemp1
Move False To iSuccess
// This example requires the Chilkat API to have been previously unlocked.
// See Global Unlock Sample for sample code.
// Chilkat recommends the following free tool for interactively examining the contents of your smart card
// through the ScMinidriver interface: MGTEK Tool for Minidriver enabled Smart Cards
// Let's first look at our smart card..
// Here's the view of our Gemalto (Thales) IDPrime MD T=0 smart card in the MGTEK tool:
// 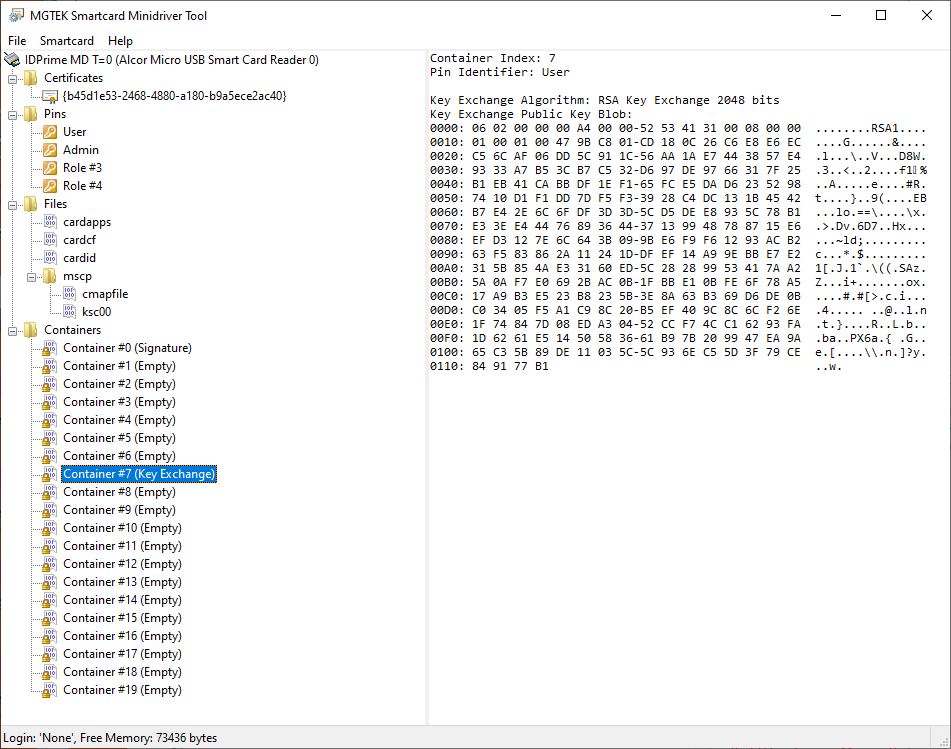 Get Create (RefClass(cComChilkatScMinidriver)) To hoScmd
If (Not(IsComObjectCreated(hoScmd))) Begin
Send CreateComObject of hoScmd
End
// First we need to acquire a context to the smart card in the reader where it is inserted.
// Reader names (smart card readers or USB tokens) can be discovered
// via List Readers or Find Smart Cards
Move "Alcor Micro USB Smart Card Reader 0" To sReaderName
Get ComAcquireContext Of hoScmd sReaderName To iSuccess
If (iSuccess = False) Begin
Get ComLastErrorText Of hoScmd To sTemp1
Showln sTemp1
Procedure_Return
End
// If successful, the name of the currently inserted smart card is available:
Get ComCardName Of hoScmd To sTemp1
Showln "Card name: " sTemp1
// We likely shouldn't need to authenticate with the smart card (use a PIN) to simply get a public key,
// so we can skip the PIN authenticatin step..
// Let's get the key(s) present in Container #7.
// In our case (shown in the image above), there is a private key in the "key exchange" position, but no key in the "signature" position.
Get Create (RefClass(cComChilkatPublicKey)) To hoPubkey_sig
If (Not(IsComObjectCreated(hoPubkey_sig))) Begin
Send CreateComObject of hoPubkey_sig
End
Get Create (RefClass(cComChilkatPublicKey)) To hoPubkey_kex
If (Not(IsComObjectCreated(hoPubkey_kex))) Begin
Send CreateComObject of hoPubkey_kex
End
Get pvComObject of hoPubkey_sig to vPubkey_sig
Get pvComObject of hoPubkey_kex to vPubkey_kex
Get ComGetContainerKeys Of hoScmd 7 vPubkey_sig vPubkey_kex To iSuccess
If (iSuccess = False) Begin
Get ComLastErrorText Of hoScmd To sTemp1
Showln sTemp1
Procedure_Return
End
Get ComEmpty Of hoPubkey_sig To bTemp1
If (bTemp1 = True) Begin
Showln "No signature key is present."
End
Else Begin
Showln "Signature key:"
Get ComGetPem Of hoPubkey_sig True To sTemp1
Showln sTemp1
End
Get ComEmpty Of hoPubkey_kex To bTemp1
If (bTemp1 = True) Begin
Showln "No Key Exchange key is present."
End
Else Begin
Showln "Key Exchange key:"
Get ComGetPem Of hoPubkey_kex True To sTemp1
Showln sTemp1
End
Get ComDeleteContext Of hoScmd To iSuccess
Showln "Success."
// Here's the output of the above sample code:
// Card name: IDPrime MD T=0
// No signature key is present.
// Key Exchange key:
// -----BEGIN RSA PUBLIC KEY-----
// MIIBCgKCAQEAsXeRhM55P13FbpNcXAMR3olbw2Wa6keZIHu5YTZYUBTlYWId+pNi
// wUz3zFIEo+0IfYR0H27ybIycQO+1IIzJofUFNMAL3tZps2OKPlsjuCPls6kXpXhv
// /gvhux8LrCtp4PcKWqJ6QVOZKChc7WAx40qFWzHi57ueqRTv3x0kESqGg/VjsqyT
// Evb55psJO2RsfhLT7+YVh3hImRM3RDaJdkTkPuOxeFyT6N7VXD09329sLuS3QkUb
// E9zEKDnz9X3d8dEQdJhSI9ba5fxl8R7fu8pB67ElfzFml96X1jLFtzy1pzOT5Fc4
// ROcaqlYckVzdBq9sxezm6MYmDBjNAcibRwIDAQAB
// -----END RSA PUBLIC KEY-----
End_Procedure