DataFlex
DataFlex
Sign PDF with Long-Term Validation (LTV Enabled)
See more PDF Signatures Examples
This example demonstrates how to a sign a PDF with long-term validation (LTV) enabled.Note: This example requires Chilkat v9.5.0.85 or greater.
Chilkat DataFlex Downloads
Use ChilkatAx-win32.pkg
Procedure Test
Boolean iSuccess
Handle hoPdf
Variant vJson
Handle hoJson
Variant vCert
Handle hoCert
String sTemp1
Move False To iSuccess
// This example requires the Chilkat API to have been previously unlocked.
// See Global Unlock Sample for sample code.
Get Create (RefClass(cComChilkatPdf)) To hoPdf
If (Not(IsComObjectCreated(hoPdf))) Begin
Send CreateComObject of hoPdf
End
// Load a PDF to be signed.
// The "hello.pdf" is available at https://chilkatsoft.com/hello.pdf
Get ComLoadFile Of hoPdf "qa_data/pdf/hello.pdf" To iSuccess
If (iSuccess = False) Begin
Get ComLastErrorText Of hoPdf To sTemp1
Showln sTemp1
Procedure_Return
End
// Options for signing are specified in JSON.
Get Create (RefClass(cComChilkatJsonObject)) To hoJson
If (Not(IsComObjectCreated(hoJson))) Begin
Send CreateComObject of hoJson
End
// In most cases, the signingCertificateV2 and signingTime attributes are required.
Get ComUpdateInt Of hoJson "signingCertificateV2" 1 To iSuccess
Get ComUpdateInt Of hoJson "signingTime" 1 To iSuccess
// Add the "ltvOcsp" instruction to the JSON passed to SignPdf.
// This is what causes Chilkat to create an LTV-enabled signature.
//
// If we are signing a PDF that already has signatures, then the existing signatures
// are automatically verified, and Chilkat will do OCSP certificate status checking (if possible)
// for those certs in existing signatures (including certs in the certificate chains)
// that do not yet have a valid OCSP response in the DSS (Document Security Store).
// Chilkat will add the OCSP responses to the /OCSPs in the Document Security Store (/DSS).
// Also, and certificates from existing signatures not yet in the DSS are added to the /Certs
// in the DSS.
//
// Also, the "ltvOcsp" causes Chilkat to add the pdfRevocationInfoArchival authenticated attribute
// to the CMS signature. The pdfRevocationInfoArchival attribute (1.2.840.113583.1.1.8)
// contains OCSP responses and the CRL for the issuer of the signing certificate.
// Therefore, Chilkat will send an OCSP request to the signing certificate's OCSP URl (if one exists)
// and will download the CRL from the issuer certificate's CRL Distribution Point (if one exists).
Get ComUpdateBool Of hoJson "ltvOcsp" True To iSuccess
// -----------------------------------------------------------------------------------
// Note: If Chilkat produces a signed PDF, but the signature is not LTV-enabled,
// the cause might be related to a failure to download CRL's or OCSP requests.
// See Possible Solution for Failure to Produce LTV-enabled PDF Signature
// -----------------------------------------------------------------------------------
// You can add the following to UncommonOptions to get detailed information about the CRL and OCSP requests
// You shouldn't set the following logging options unless there is a need, because it adds a large amount of information to the LastErrorText.
Set ComUncommonOptions Of hoPdf To "LOG_OCSP_HTTP,LOG_CRL_HTTP"
// Define the appearance of the signature.
Get ComUpdateInt Of hoJson "page" 1 To iSuccess
Get ComUpdateString Of hoJson "appearance.y" "top" To iSuccess
Get ComUpdateString Of hoJson "appearance.x" "left" To iSuccess
Get ComUpdateString Of hoJson "appearance.fontScale" "10.0" To iSuccess
Get ComUpdateString Of hoJson "appearance.text[0]" "Digitally signed by: cert_cn" To iSuccess
Get ComUpdateString Of hoJson "appearance.text[1]" "current_dt" To iSuccess
Get ComUpdateString Of hoJson "appearance.text[2]" "This is an LTV-enabled signature." To iSuccess
// Load the signing certificate. (Use your own certificate.)
Get Create (RefClass(cComChilkatCert)) To hoCert
If (Not(IsComObjectCreated(hoCert))) Begin
Send CreateComObject of hoCert
End
Get ComLoadPfxFile Of hoCert "qa_data/pfx/myPdfSigningCert.pfx" "pfxPassword" To iSuccess
If (iSuccess = False) Begin
Get ComLastErrorText Of hoCert To sTemp1
Showln sTemp1
Procedure_Return
End
// Tell the pdf object to use the certificate for signing.
Get pvComObject of hoCert to vCert
Get ComSetSigningCert Of hoPdf vCert To iSuccess
If (iSuccess = False) Begin
Get ComLastErrorText Of hoPdf To sTemp1
Showln sTemp1
Procedure_Return
End
Get pvComObject of hoJson to vJson
Get ComSignPdf Of hoPdf vJson "qa_output/hello_ltv_signed.pdf" To iSuccess
If (iSuccess = False) Begin
Get ComLastErrorText Of hoPdf To sTemp1
Showln sTemp1
Procedure_Return
End
Showln "The PDF has been successfully cryptographically signed with long-term validation."
// If you open the Signature Panel in Adobe Acrobat, it will indicate that the signature is LTV enabled
// as shown here:
// 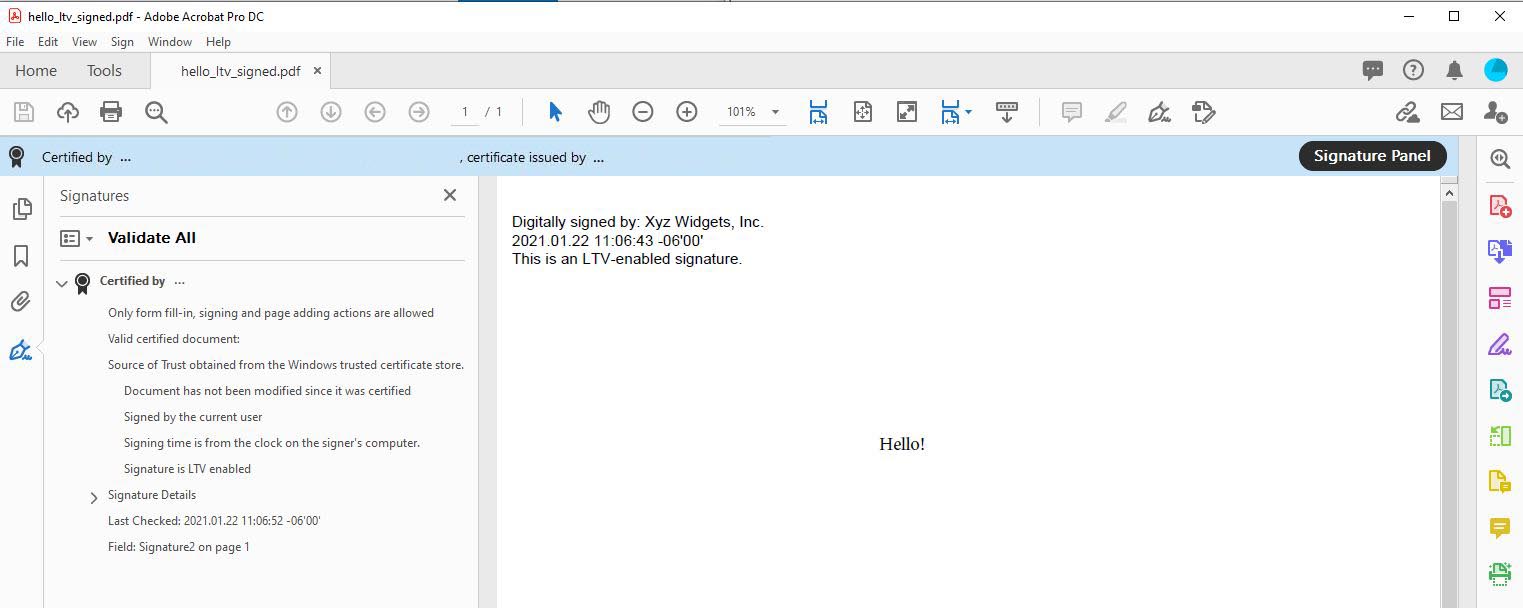 End_Procedure